Create and preserve value by protecting intellectual property, mitigating critical cyber risk, complying with regulatory requirements and enhancing cyber resilience.
As Mergers & Acquisitions (M&A) and startup investments become central to business growth, efforts typically focus on revenue, systems, people, and profitability. However, cybersecurity and regulatory compliance are often overlooked. Neglecting these areas can lead to data breaches, cyberattacks, which can undermine returns, damage reputations, and erode shareholder trust.
This overview highlights the importance of securing intellectual property, safeguarding data, and managing cyber and compliance risks during M&A and investment activities.
Read the full article
AI, OSINT, and HUMINT: A Combined Approach to Global Asset Tracing in Litigation, Arbitration, and Judgment Enforcement
September 28, 2026
Director Dominika Jaskiewicz's latest Raising the Bar article explores how OSINT, HUMINT, and AI combine to uncover hidden assets in cross-border litigation, arbitration, and judgment enforcement.
A New Frontier: The Changing Face of Regulation in English Football
September 22, 2026
In our first episode, Managing Director Jon Brown interviews new Senior Advisor Adam Crockett to discuss the changing regulatory landscape of English Football. The second half of their discussion will be published next month.
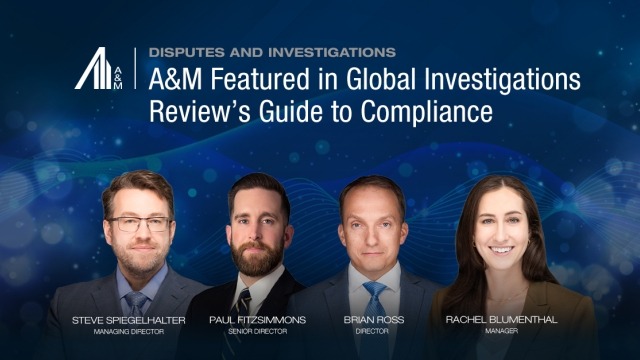
GIR Guide to Compliance: Compliance programme monitoring and auditing: demonstrating effectiveness under regulatory scrutiny
September 17, 2026
Compliance programs are only as strong as your ability to prove they work. Steve Spiegelhalter, Paul Fitzsimmons, Brian Ross, and Rachel Blumenthal outline how effective monitoring and auditing help companies demonstrate program effectiveness under regulatory scrutiny.